
Chapters & navigation
START HERE
Architecture
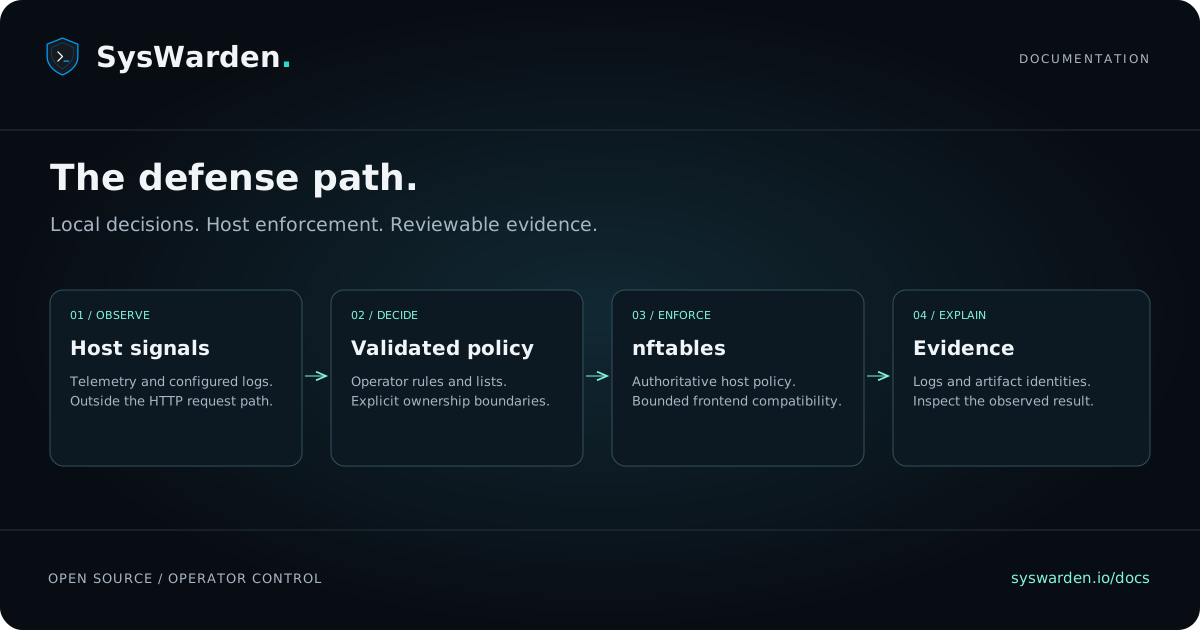
Understand how local signals, explicit policy, nftables enforcement and retained evidence fit together.
On this page
SysWarden combines local observation, explicit policy and host firewall enforcement. Start with the boundaries: it is a Linux host security orchestrator, not an inline HTTP proxy or a regulatory certification product.
Observe: keep the source visible#
Host telemetry and configured security logs provide signals. Upstream web protection remains in its own request path. SysWarden analyzes supported logs out of band; it does not proxy or sanitize application traffic.
Decide: validate before changing policy#
Operator configuration, bounded threat-intelligence lists and validated observations feed policy decisions. Keep the origin and version of each configuration visible. An enrichment label is context, not independent authority to modify a firewall.
Enforce: one authoritative policy#
The host's nftables policy is the enforcement boundary. When exactly one supported firewall frontend is already active, SysWarden can reconcile its bounded owned rules through the documented compatibility path. Preserve operator-owned rules and verify real access after changes.
Retain evidence: explain what happened#
Logs, package identities, source revisions and release evidence connect observed behavior to the exact software that produced it. The local terminal interface supports operations without introducing a browser terminal or a network listener for the TUI.
Connect BunkerWeb at the right boundary#
BunkerWeb handles web traffic in band. Its optional integration submits authenticated operations to SysWarden through the documented HA API. Authorization, ownership, freshness and cleanup rules remain explicit. Read the complete BunkerWeb integration contract before enabling it.
Separate HA capability from an operational claim#
HA involves peer identity, TLS, authorization, durable state and recovery. A successful local configuration or a green CI check is not a native endurance campaign. The v4.10.0 IVV record distinguishes current functional checks from historical endurance evidence.
Read the implementation#
This overview is conceptual. For exact behavior, use the published source, the operator reference and the version-specific procedures in this documentation.